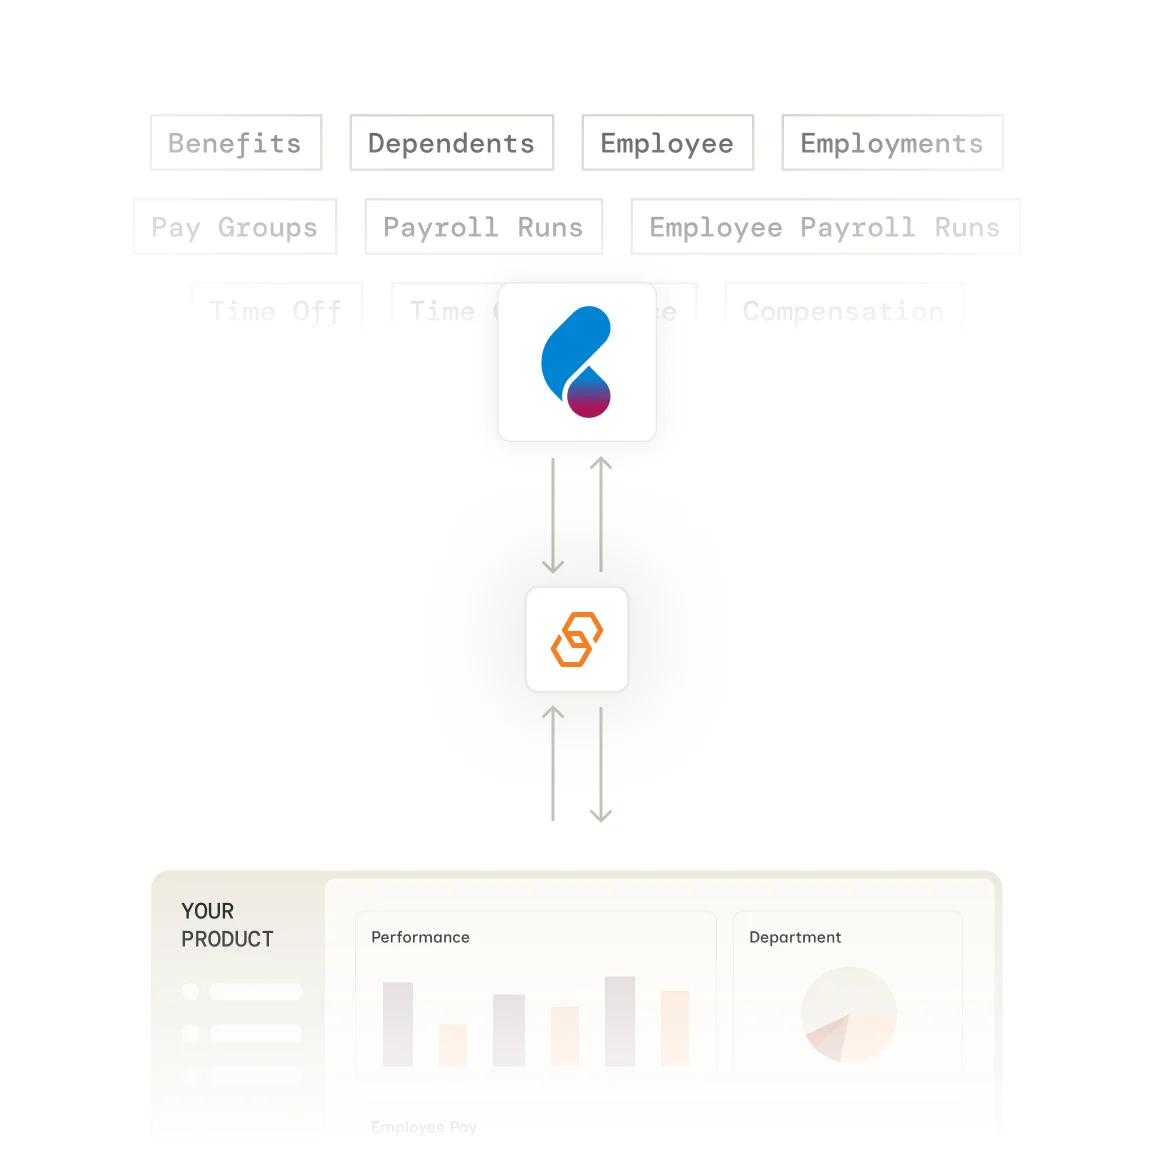
Stop building Cezanne HR integrations from scratch. Bindbee gives you a single API to sync Cezanne HR employee records, compensation, job history, org structure, and time-off requests—without the maintenance headaches.


Bindbee normalizes Cezanne HR's data into our unified models. One integration, consistent data structure across 110+ HR systems.
Authenticate via Magic Link—our drop-in auth component. Your customer logs in to Cezanne HR and grants access in minutes.
We normalize Cezanne HR data to unified models with automatic incremental syncs. Employee, compensation, time off, and groups data stays fresh.
One REST API for Cezanne HR and 110+ other HR systems. Same endpoints, same data structure, regardless of your customer's payroll provider.

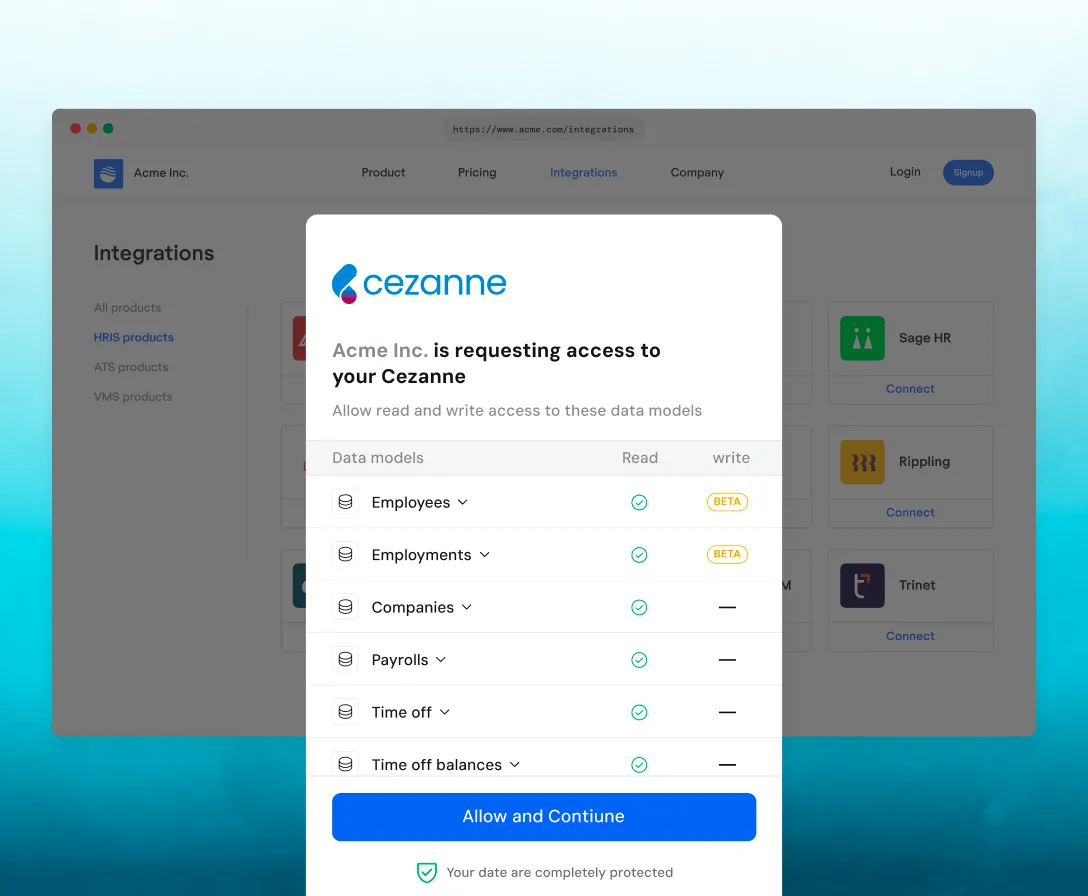
Customers authenticate effortlessly via Magic Link, with an embeddable SDK that enables seamless, in-app connections.
A Client ID and Client Secret from an authorised application in Cezanne (Administration → Security Settings → Authorised Applications) with read scopes. Bindbee handles the OAuth token exchange.
Bindbee syncs Cezanne employee records, including name, preferred_name, employee_number, work_email, mobile_phone_number, date_of_birth, gender, ethnicity, department, designation, manager, start_date, termination_date, termination_reason, and tobacco_use.
Yes. Custom fields are returned in the custom_fields object on the Employee model.
Yes. The Compensation model returns pay_rate, pay_period, pay_currency, and start_date for each employee.
Yes. The Time Off model returns request_type, status, start_time, end_time, amount, units, the employee_note, and the approver.
Yes. Groups come with name, type, parent_group, and is_commonly_used_as_team, and the manager field gives reporting lines.
Yes. Check employment_status, termination_date, and termination_reason to identify leavers.
You don't. Bindbee manages token refresh and rate limiting, caches data, and retries failures automatically.
Yes. Bindbee is SOC 2 Type II certified, ISO 27001 certified, HIPAA compliant, and GDPR ready. Data is encrypted in transit and at rest, and we never store your customer's credentials on your servers.


We use cookies to improve your experience on our site. By using our site, you are agreeing to the collection and use of data as described in our privacy policy.