Stop building Namely integrations from scratch. Bindbee gives you a single API to sync Namely employee profiles, demographics, compensation, teams, and office locations—without the maintenance headaches.


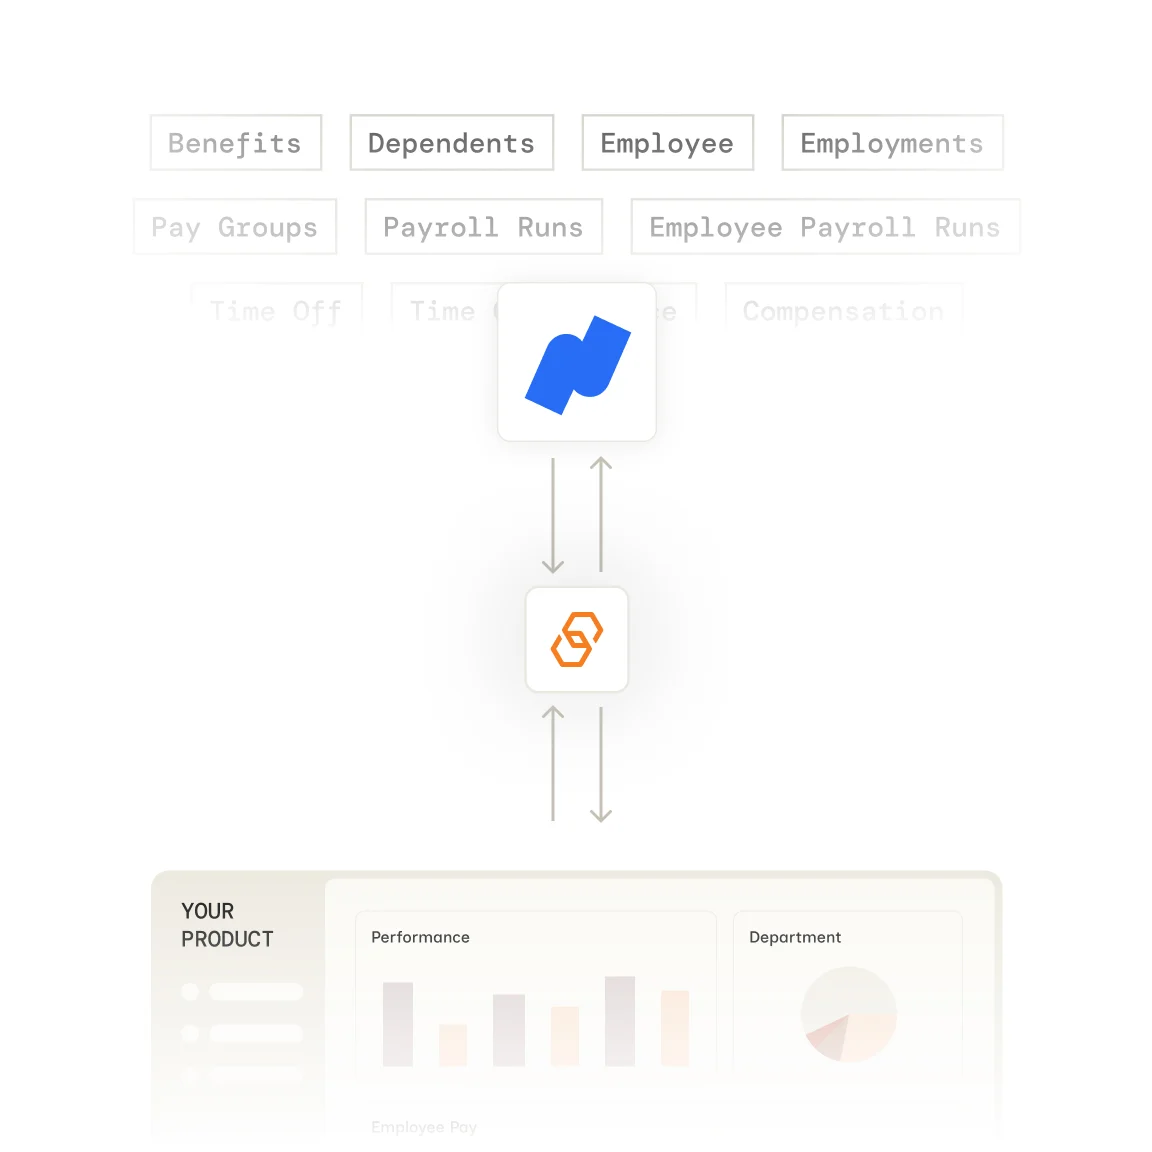
Bindbee normalizes Namely's data into our unified models. One integration, consistent data structure across 102+ HR systems.
Authenticate via Magic Link—our drop-in auth component. Your customer logs in to Namely and grants access in minutes.
We normalize Namely data to unified models with automatic incremental syncs. Employee, compensation, company, group, and location data stays fresh.
One REST API for Namely and 102+ other HR systems. Same endpoints, same data structure, regardless of your customer's payroll provider.

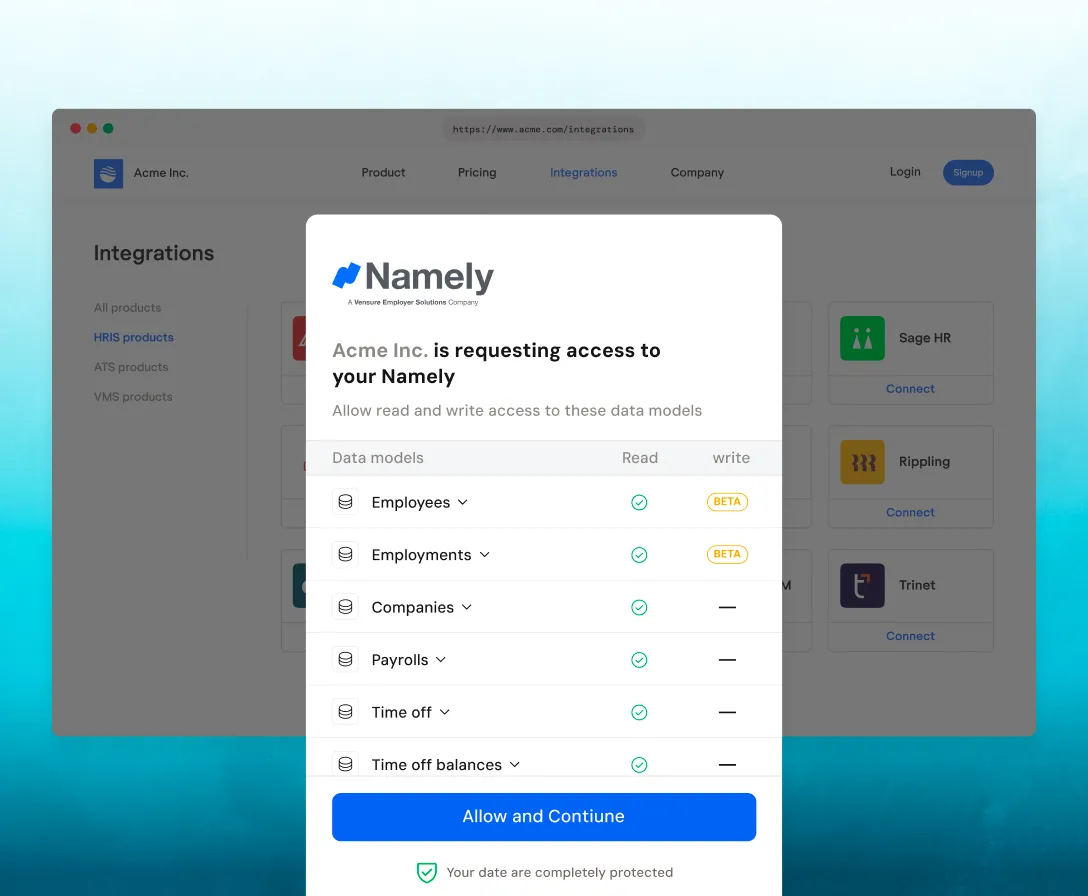
Customers authenticate effortlessly via Magic Link, with an embeddable SDK that enables seamless, in-app connections.
Most customers complete setup in under 10 minutes. A Namely admin connects through Magic Link, and the initial sync starts immediately.
A Namely administrator account and the company's Namely subdomain. Admins can create a personal access token from the API page in their Namely profile, and Magic Link walks them through it.
Bindbee syncs Namely profiles with 30 employee fields, including name, preferred_name, employee_number, work and personal email, phone numbers, date_of_birth, gender, ethnicity, marital_status, ssn, department, designation, manager, start_date, and home and work addresses.
Yes. The Compensation model returns pay_rate, pay_period, pay_currency, and start_date for each employee.
Namely groups and teams come through the Group model with name, type, and is_commonly_used_as_team. Employees are linked to them via groups.
Yes. The Location model returns full addresses (name, street_1, street_2, city, state, postal_code, country), and employees are linked via work_locations.
Yes. Filter by employment_status=INACTIVE or check termination_date and termination_reason. Historical profiles remain accessible.
You don't. Bindbee manages requests to Namely's API, caches data, and retries failed requests automatically.
Yes. Bindbee is SOC 2 Type II certified, ISO 27001 certified, HIPAA compliant, and GDPR ready. Data is encrypted in transit and at rest, and we never store your customer's credentials on your servers.


We use cookies to improve your experience on our site. By using our site, you are agreeing to the collection and use of data as described in our privacy policy.